
Eliminate HTTPS Warnings for Your Local Domain with Centralized Trust
Seamlessly secure your internal websites and ensure client trust across your Azure AD environment.
Key Insights for Local Domain Certification
- Establish an Internal Certificate Authority (CA): Public CAs do not issue certificates for non-public local domains (e.g., .local). Creating your own internal CA is essential for generating trusted certificates for your internal websites.
- Centralized Certificate Distribution: To avoid manual configuration on every client PC, leverage Group Policy for on-premises Active Directory (AD) joined devices or Microsoft Intune for Azure AD-joined devices to automatically distribute your internal CA's root certificate.
- Azure AD Integration: While Azure AD primarily handles identity management, the trust for local domain certificates is managed at the operating system level. Intune serves as the primary tool for deploying trusted root certificates to devices managed by Azure AD.
Certifying a local domain website for network-joined clients to eliminate annoying security warnings, especially when using Azure AD, is not only possible but also a best practice for internal security and user experience. The key is to move away from self-signed certificates, which are inherently untrusted by browsers, towards a managed internal Public Key Infrastructure (PKI).
This comprehensive guide will detail how to achieve this, focusing on creating your own Certificate Authority (CA) and leveraging centralized distribution methods to ensure all your client PCs automatically trust your internal website.
Understanding the Challenge with Self-Signed Certificates
When you access a website secured with a self-signed certificate, your browser displays a warning because it cannot verify the certificate's authenticity through a recognized Certificate Authority. This is because self-signed certificates lack a chain of trust back to a widely trusted root CA. For internal networks, relying solely on self-signed certificates leads to security alerts, which can erode user confidence and prompt users to bypass warnings, potentially exposing them to risks.
For domains like .local or other internal-only names, public CAs cannot issue certificates because these domains are not publicly resolvable or verifiable. Therefore, the solution lies in establishing your own internal CA. This internal CA will issue certificates for your local domain websites, and by distributing the CA's root certificate to your client machines, you create an internal chain of trust.
Establishing Your Internal Certificate Authority (CA)
The first fundamental step is to set up a Certificate Authority within your organization. This internal CA will be responsible for issuing and managing certificates for your internal web resources. Windows Server provides robust Active Directory Certificate Services (AD CS) for this purpose, but open-source alternatives like OpenSSL can also be used.
Choosing Your Internal CA Platform
Windows Server Active Directory Certificate Services (AD CS)
If your environment primarily uses Windows Server and Active Directory, AD CS is the recommended choice. It integrates seamlessly with your existing infrastructure, simplifying certificate management and deployment.
Here’s a general overview of the steps:
- Installation: Install the "Active Directory Certificate Services" role on a dedicated server or a domain controller.
- Configuration: Configure it as an Enterprise Root CA or a Standalone Root CA, depending on your network's size and complexity. For most internal networks, an Enterprise Root CA is suitable as it integrates with Active Directory.
- Policy Modules: Ensure the CA is configured to issue certificates that meet your organization's security policies.
Video: Deploy Certificate Services & Enterprise Root Certification Authority. This video is an excellent resource for setting up your internal CA in a Windows Server environment. It guides you through the process of installing and configuring Active Directory Certificate Services, which is foundational for issuing trusted certificates for your local domain website.
OpenSSL for Custom CA
For Linux-based environments or if you prefer a non-Windows solution, OpenSSL can be used to create a custom CA. This provides flexibility but requires more manual configuration.
- Generate Root CA Key and Certificate: Use OpenSSL commands to create a private key and a self-signed root certificate for your internal CA. This root certificate will be the anchor of trust for all certificates issued by your CA.
openssl genrsa -des3 -out rootCA.key 2048
openssl req -x509 -new -nodes -key rootCA.key -sha256 -days 1024 -out rootCA.crt
Issuing SSL Certificates for Your Local Website
Once your internal CA is operational, you can use it to issue SSL certificates for your local domain website. This certificate will be signed by your internal CA, linking its trust back to your root CA.
Generating a Certificate Signing Request (CSR)
On your web server, you'll generate a Certificate Signing Request (CSR). This CSR contains information about your website, such as its fully qualified domain name (FQDN), organization details, and public key.
- For Windows Servers (IIS): Use the IIS Manager to create a new certificate request.
- For Linux Servers (Apache/Nginx with OpenSSL): Use OpenSSL commands:
openssl genrsa -out yourwebsite.key 2048
openssl req -new -key yourwebsite.key -out yourwebsite.csr
Ensure the Common Name (CN) in the CSR exactly matches your local domain FQDN (e.g., intranet.yourdomain.local). Also, include Subject Alternative Names (SANs) for any other hostnames or IP addresses that clients might use to access the website.
Signing the Certificate Request
Submit the generated CSR to your internal CA. The CA will then sign the request using its private key, issuing a new certificate that is trusted by your internal CA.
- For AD CS: Use the Certificate snap-in or the web enrollment page to request and issue the certificate.
- For OpenSSL CA: Sign the CSR using your root CA's private key:
openssl x509 -req -in yourwebsite.csr -CA rootCA.crt -CAkey rootCA.key -CAcreateserial -out yourwebsite.crt -days 365 -sha256 -extfile yourwebsite.ext
The yourwebsite.ext file would contain the subjectAltName extension for SANs.
Installing and Configuring the Certificate on Your Web Server
Once you have the signed certificate (e.g., yourwebsite.crt or a .pfx file containing both certificate and private key), install it on your web server and configure your web server software (IIS, Apache, Nginx) to use it for HTTPS.
This involves binding the certificate to your website and ensuring the website listens on port 443 for HTTPS traffic.
Centralized Distribution of Root CA Certificate to Client PCs
This is the most critical step to avoid manual tinkering on each client PC. By distributing your internal CA's root certificate to the "Trusted Root Certification Authorities" store on client machines, you ensure they automatically trust any certificate issued by your CA.
Leveraging Group Policy for On-Premises AD-Joined Clients
If your client PCs are joined to an on-premises Active Directory domain, Group Policy Objects (GPOs) are the most efficient method for mass distribution.
- Export the Root CA Certificate: Export your internal CA's root certificate (e.g.,
rootCA.crt) in a suitable format (DER or Base-64 encoded X.509). - Create/Edit a GPO: Open the Group Policy Management Console (GPMC) on your domain controller. Create a new GPO or edit an existing one that applies to your client computers.
- Import the Certificate: Navigate to Computer Configuration > Policies > Windows Settings > Security Settings > Public Key Policies > Trusted Root Certification Authorities. Right-click and select "Import" to add your root CA certificate.
- Link and Enforce GPO: Link the GPO to the appropriate Organizational Unit (OU) containing your client computers. Run
gpupdate /forceon client machines (or wait for policy refresh) to apply the changes.
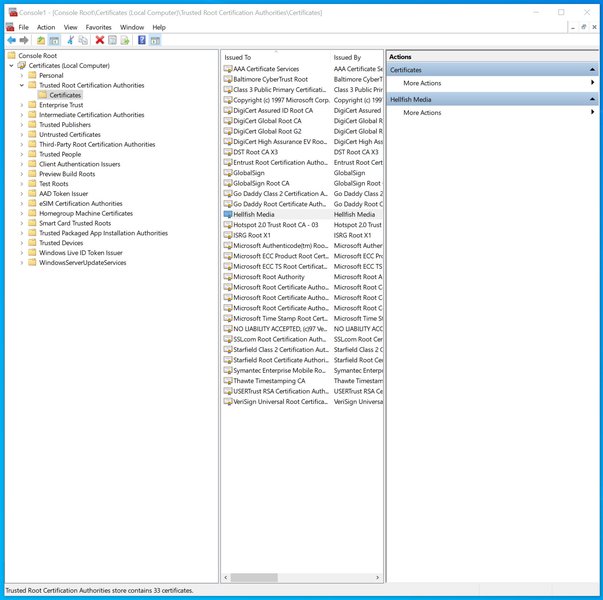
Image: A screenshot of the Windows 10 Trusted Root Certification Authorities store, where your internal CA's root certificate will be imported to ensure system-wide trust.
Deploying Certificates with Microsoft Intune for Azure AD-Joined Clients
Since you are using Azure AD, Microsoft Intune (part of Microsoft Endpoint Manager) is the primary tool for managing and deploying configurations to Azure AD-joined devices (including hybrid Azure AD join or pure Azure AD join). Intune can deploy your internal CA's root certificate to these devices automatically.
- Create a Trusted Certificate Profile: In the Microsoft Endpoint Manager admin center, navigate to Devices > Configuration profiles. Create a new profile for "Trusted certificate (Windows 10 and later)" or similar.
- Upload Root CA Certificate: Upload your exported root CA certificate (e.g.,
rootCA.ceror.crt) to the profile. - Assign Profile: Assign this profile to the Azure AD device group(s) containing your client computers. Intune will then push this certificate to all targeted devices, installing it into their Trusted Root Certification Authorities store.
This method ensures that even devices solely managed by Azure AD will trust certificates issued by your internal CA, eliminating the need for individual client configuration.
Evaluating Your Certificate Trust Environment
Understanding the interplay between your internal CA, client types, and distribution methods is crucial for a robust security posture. This radar chart illustrates the effectiveness of various certificate management strategies in different environments.
This radar chart illustrates the strengths and weaknesses of different certificate management approaches for local domain websites. "Internal CA + Group Policy" excels in automation and scalability for on-premises AD environments. "Internal CA + Intune" shines in Azure AD integration and automation for cloud-managed devices. In contrast, "Self-Signed Certificate (Manual Trust)" offers high cost-effectiveness but severely lacks in scalability, automation, and security confidence, highlighting why transitioning to an internal CA is crucial for a professional internal network setup.
Key Considerations and Best Practices
Implementing an internal PKI requires careful planning to ensure security, efficiency, and continuous trust.
Renewal and Automation
Certificates have expiration dates. Develop a strategy for renewing both your internal CA's root certificate and the website's SSL certificates before they expire to avoid service disruption. Automation tools or scripts can help streamline this process.
Certificate Revocation Lists (CRLs) and Online Certificate Status Protocol (OCSP)
For enhanced security, your CA should publish Certificate Revocation Lists (CRLs) or support Online Certificate Status Protocol (OCSP) to allow clients to verify the revocation status of certificates. This is crucial if a private key is compromised.
Integration with Azure Services
While the primary focus is on internal websites, if your local domain website needs to interact with Azure App Services or other Azure cloud resources (e.g., calling an internal API from an Azure-hosted application), you might need to configure those Azure services to trust your internal CA. This often involves uploading the root CA certificate to Azure Key Vault and then configuring the App Service to load it.
Visualizing the PKI Ecosystem
The following mindmap illustrates the interconnected components and concepts involved in certifying a local domain website with an internal CA and distributing trust to clients, especially in an Azure AD-integrated environment.
This mindmap visually represents the comprehensive process of certifying a local domain website, from understanding the initial problem of self-signed certificates to implementing an internal Certificate Authority and distributing its root certificate to various client types. It highlights the critical roles of Group Policy for on-premises AD and Intune for Azure AD-joined environments, demonstrating how these tools enable automated, centralized trust management.
Comparison of Certificate Distribution Methods
The following table summarizes the key characteristics of different certificate distribution methods, providing a quick reference for your specific environment and needs.
| Method | Target Clients | Pros | Cons | Azure AD Relevance |
|---|---|---|---|---|
| Self-Signed (Manual Import) | Any PC (manual per device) | No external CA needed, simplest to generate initially. | High manual effort, untrusted by default, poor scalability, security warnings. | Not directly managed by Azure AD; highly inefficient for more than a few devices. |
| Internal CA + Group Policy | On-premises AD-joined PCs | Automated, scalable for domain-joined clients, centralized management. | Requires on-premises Active Directory infrastructure. | Effective for hybrid Azure AD environments where devices are still AD-joined. |
| Internal CA + Microsoft Intune | Azure AD-joined PCs (including Hybrid) | Automated, scalable for cloud-managed devices, ideal for modern workspaces. | Requires Intune licensing, setup complexity, might not cover all legacy scenarios. | Primary method for distributing certificates to pure Azure AD-joined devices. |
| Public CA (e.g., Let's Encrypt) | Publicly accessible PCs | Globally trusted, automatic renewal (ACME), free/low cost. | Cannot issue certificates for non-public (internal-only) domains like .local. |
Not applicable for local domain websites unless they are publicly resolvable. |
Frequently Asked Questions (FAQ)
Why can't I use a public Certificate Authority for my local domain website?
.local) are not publicly resolvable on the internet, public CAs cannot verify them and thus will not issue certificates for them. Internal CAs are specifically designed for this purpose.What is the difference between an Enterprise Root CA and a Standalone Root CA in Windows Server?
How does Azure AD fit into this? Does it handle certificate trust directly?
My clients are a mix of Windows, macOS, and Linux. How do I distribute the root CA certificate to all of them?
/etc/ssl/certs directory. For macOS, certificates can be imported into the Keychain Access utility and marked as trusted.Conclusion
Certifying a local domain website to eliminate security warnings is a critical step for improving the security and user experience of your internal network. By implementing your own internal Certificate Authority and leveraging centralized distribution mechanisms like Group Policy for on-premises AD environments or Microsoft Intune for Azure AD-joined clients, you can ensure that all your network-joined devices automatically trust your internal website's SSL certificate. This approach scalable, professional, and eliminates the need for time-consuming manual configuration on each individual client PC, providing a seamless and secure browsing experience for your users.
Recommended Further Exploration
- How to configure Active Directory Certificate Services for internal PKI
- Deploying trusted root certificates using Microsoft Intune
- Best practices for internal certificate authority management
- Troubleshooting SSL certificate trust issues in internal networks
Referenced Search Results
 cdn.deliciousbrains.com