
Transitioning Your Google App Engine Application to Cloudflare: A Comprehensive Guide
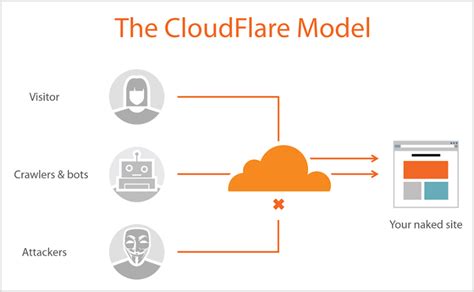
Migrating your application from Google App Engine (GAE) to Cloudflare can enhance your website's performance, security, and reliability. This transition involves several critical steps, particularly concerning DNS management and SSL certificate configuration. This guide provides a detailed roadmap to ensure a smooth and secure migration without unnecessary complications.
1. Understanding Your Current Setup
a. Google App Engine (GAE)
Google App Engine is a fully managed, serverless platform designed for developing and hosting web applications. One of its standout features is the automatic management of SSL certificates for custom domains, ensuring secure HTTPS connections without manual intervention. GAE's managed SSL certificates auto-renew and require minimal maintenance, providing a hassle-free experience for developers.
b. SSL Certificates in GAE
GAE handles SSL certification through Google-managed certificates, which automatically renew and deploy updates seamlessly. This built-in feature simplifies the process of maintaining secure connections, allowing developers to focus on application development rather than certificate management.
2. Benefits of Switching to Cloudflare
a. Enhanced Performance
Cloudflare boasts a global Content Delivery Network (CDN) that caches your content closer to end-users. This geographical distribution significantly reduces latency and improves load times, enhancing the overall user experience.
b. Superior Security Features
Cloudflare offers robust security measures, including DDoS protection, Web Application Firewall (WAF), and advanced bot management. These features safeguard your application from a wide array of threats, ensuring data integrity and availability.
c. Advanced SSL Management
With Cloudflare, you gain access to flexible SSL options and granular control over SSL settings. This flexibility allows for tailored security configurations that align with your application's specific needs.
d. Additional Features
Cloudflare provides a suite of additional tools such as analytics, image optimization, and automatic HTTPS rewrites. These features contribute to both the performance and operational efficiency of your application.
3. Steps to Switch to Cloudflare
a. Create a Cloudflare Account and Add Your Domain
-
Sign Up for Cloudflare: If you don't already have an account, visit the Cloudflare Sign-Up Page and create one.
-
Add Your Domain: Once logged in, add your domain by entering it in the designated field. Cloudflare will initiate a scan of your existing DNS records.
-
Review DNS Records: Ensure that all necessary DNS records (A, CNAME, MX, etc.) are accurately imported. Pay special attention to CNAME records pointing to
ghs.googlehosted.comfor Google App Engine deployments.
b. Update Nameservers
-
Obtain Cloudflare Nameservers: After adding your domain, Cloudflare will provide you with two unique nameservers (e.g.,
lara.ns.cloudflare.comandmike.ns.cloudflare.com). -
Update at Your Domain Registrar: Log in to your domain registrar's dashboard (e.g., Google Domains) and replace the existing nameservers with the ones provided by Cloudflare. This action delegates DNS management to Cloudflare.
-
Propagation Time: DNS changes can take anywhere from a few minutes to 48 hours to propagate globally. During this period, your website may experience intermittent availability.
c. Configure SSL Settings on Cloudflare
Cloudflare SSL Modes
Cloudflare offers four SSL modes, each providing different levels of encryption and security:
- Off: No SSL; traffic between users and your site is not encrypted.
- Flexible: Encrypts traffic between users and Cloudflare only.
- Full: Encrypts traffic between users and Cloudflare, and between Cloudflare and your origin server (GAE) using any SSL certificate.
- Full (Strict): Encrypts traffic end-to-end, with Cloudflare validating the origin server’s SSL certificate.
Recommended SSL Mode: Full (Strict)
For optimal security, it is recommended to use Full (Strict) SSL mode. This mode ensures that all connections are encrypted and that the SSL certificate on your origin server is valid and trusted.
d. Generating and Installing SSL Certificates
Option 1: Using Google-Managed SSL Certificates
-
Verify SSL Certificate: Ensure that your GAE application is utilizing Google-managed SSL certificates. These certificates automatically renew and are trusted by Cloudflare.
-
Configure Cloudflare: Set Cloudflare’s SSL mode to Full (Strict). This configuration leverages the existing Google-managed certificates without requiring new certificates.
-
Potential Issues: In some cases, especially with subdomains or wildcard certificates, Google-managed certificates might not perfectly align with Cloudflare's strict validation, necessitating further configuration.
Option 2: Using Cloudflare Origin Certificates
-
Generate Origin Certificate: In the Cloudflare dashboard, navigate to SSL/TLS > Origin Server and click on Create Certificate.
-
Download Certificates: Select to generate a private key and CSR, define the domains to cover, and download both the Origin Certificate and Private Key.
-
Upload to GAE: Go to the Google Cloud Console, navigate to App Engine > Settings > SSL Certificates, and upload the downloaded Origin Certificate and Private Key.
-
Activate Full (Strict) SSL: Ensure that Cloudflare’s SSL mode is set to Full (Strict) to validate the origin certificate.
Considerations When Using Origin Certificates
- Security: Origin Certificates are trusted only by Cloudflare, adding an extra layer of security by ensuring that only Cloudflare can communicate with your origin server.
- Automatic Renewal: While Cloudflare manages the lifecycle of these certificates, integrating them with GAE may require manual updates depending on your configuration.
- GAE Compatibility: According to certain sources, Cloudflare Origin Certificates might not be fully supported by GAE, potentially necessitating the use of third-party SSL certificates.
4. Do You Need to Request New SSL Certificates?
The necessity of requesting new SSL certificates hinges on your chosen SSL configuration mode within Cloudflare:
a. Using Google-Managed SSL Certificates
- If you opt for Full (Strict) SSL mode and your GAE-managed certificates are valid and correctly configured, you likely do not need to request new SSL certificates. Cloudflare will validate the existing certificates, maintaining end-to-end encryption.
- However, if there are issues with certificate alignment, especially concerning subdomains or wildcard certificates, you may need to acquire compatible SSL certificates to ensure seamless validation.
b. Using Cloudflare Origin Certificates
- Implementing Full (Strict) SSL mode with Cloudflare Origin Certificates typically requires generating new certificates through Cloudflare. These certificates ensure secure communication between Cloudflare and your GAE application.
- Given potential compatibility issues with GAE, you might need to explore third-party SSL certificates that are universally trusted and compatible with both Cloudflare and GAE.
In summary, while leveraging existing Google-managed SSL certificates is feasible, ensuring full compatibility and adherence to Cloudflare’s strict validation standards may necessitate the acquisition of new SSL certificates.
5. Potential Challenges and Considerations
a. Certificate Compatibility
Ensuring that SSL certificates are compatible between Cloudflare and GAE is paramount. Misalignment can lead to validation failures, resulting in insecure connections or downtime.
b. DNS Propagation Delays
Updating nameservers involves DNS propagation, which can take up to 48 hours. During this period, your website may experience intermittent availability or inconsistent behavior.
c. Configuration Complexity
Managing SSL across two platforms—Cloudflare and GAE—requires meticulous configuration to prevent security gaps or conflicts. This dual management can introduce complexity, especially for those unfamiliar with SSL certificate nuances.
d. Renewal and Maintenance
While Cloudflare can manage Origin Certificate renewals, integrating these with GAE may necessitate manual updates, depending on your setup. This requirement adds an additional layer of maintenance responsibility.
e. Limitation on Managed SSL Certificates
Google App Engine, utilizing Let’s Encrypt for managed certificates, imposes limits, such as a maximum of 50 managed certificates per week per base domain. This constraint requires careful planning to avoid hitting issuance limits during migration.
6. Testing and Validation
a. Verify SSL Configuration
After configuring SSL settings, use tools like SSL Labs' SSL Test to verify the integrity and correctness of your SSL setup. This step ensures that your certificates are correctly installed and that there are no vulnerabilities.
b. Ensure HTTPS Redirection
Confirm that all HTTP requests are seamlessly redirected to HTTPS. This redirection is crucial for maintaining secure connections and ensuring that users always interact with your site over encrypted channels.
c. Test Across Multiple Regions
Given Cloudflare's global infrastructure, it's essential to test your application’s accessibility and performance from different geographic locations. This testing ensures that the CDN is functioning correctly and that users worldwide experience optimal performance.
d. Monitor Performance and Security
Utilize Cloudflare's analytics tools to monitor traffic patterns, performance metrics, and security events. Continuous monitoring allows you to identify and address potential issues proactively.
7. Best Practices
-
Start with DNS-Only Mode: While testing, consider using Cloudflare's DNS-only mode to ensure that your application remains accessible without immediately activating Cloudflare's proxy services.
-
Complete Domain Verification: Ensure that your GAE domain verification is fully completed before making any DNS changes. This verification prevents potential access issues during the migration.
-
Maintain Existing SSL Configurations: Keep your current SSL configurations active until Cloudflare is fully integrated. This practice ensures uninterrupted secure access to your application.
-
Implement a Staging Environment: Use a staging environment to test the Cloudflare setup before rolling it out to your production environment. This approach minimizes the risk of unforeseen issues impacting your live application.
8. Additional Resources
9. Conclusion
Migrating your application from Google App Engine to Cloudflare is a manageable process that can significantly enhance both performance and security. The transition primarily involves updating DNS settings and configuring SSL certificates to maintain secure and reliable connections.
To ensure optimal security, especially when using Full (Strict) SSL mode, consider the following:
- Generating a New Origin Certificate from Cloudflare: This step ensures that communication between Cloudflare and your GAE application is securely encrypted and trusted.
- Uploading the Certificate to Google App Engine: Proper installation of the Origin Certificate on GAE is crucial for the Full (Strict) SSL mode to function correctly.
While the process requires careful planning and execution, the benefits of enhanced security, improved performance, and advanced features make the effort worthwhile. For those handling sensitive data, implementing Full (Strict) SSL with Cloudflare Origin Certificates is highly recommended to maintain a strong security posture.
Alternatively, if you prefer a simpler setup and are willing to accept slightly reduced security, you can opt for Cloudflare's Full SSL mode without uploading new certificates. This choice allows continued use of Google-managed certificates while benefiting from Cloudflare's performance and basic security features.
Ultimately, a well-executed migration to Cloudflare will provide your Google App Engine application with enhanced capabilities, ensuring a secure and efficient experience for your users.
Last updated January 7, 2025