
Cloud Security: On-Premise vs. Cloud Environments
Exploring the differences, benefits, and challenges in securing IT infrastructures
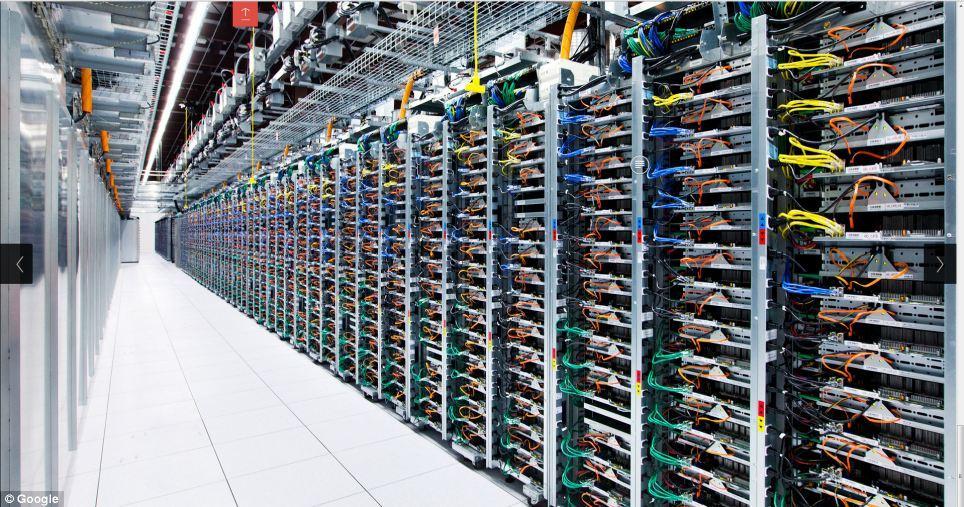
Key Highlights
- Control and Customization: On-premise offers unparalleled direct management, while cloud relies on standardized, provider-managed security.
- Scalability and Cost Flexibility: Cloud environments excel in scalability and cost efficiency, contrasted with the high upfront investment in on-premise systems.
- Compliance and Reliability: Both approaches have unique strengths in meeting regulatory requirements, with on-premise allowing strict adherence and cloud offering robust maintenance and redundancy.
Understanding the Security Paradigms
When comparing security in on-premise infrastructure versus cloud environments, it is essential to understand that each method has unique strengths and trade-offs. The decision largely depends on an organization’s requirements regarding control, cost, scalability, regulatory compliance, and overall risk management. Both approaches have evolved to address the growing complexity of cybersecurity threats and ensure the integrity, confidentiality, and availability of critical data.
On-Premise Security: Full Control, Custom Environment
On-premise security involves hosting data, applications, and IT resources directly within an organization’s own data centers or server rooms. This model grants the organization complete control over all aspects of its security environment—from physical access to network infrastructure and software configurations.
Control and Customization
One of the most significant benefits of on-premise security is the unparalleled control that it offers. Organizations can implement and adjust security protocols to address specific vulnerabilities that are unique to their operational environments. Customized firewall configurations, intrusion detection systems, and strict physical access controls allow IT teams to tailor their defenses precisely.
The ability to directly manage every component in the security stack can be particularly advantageous in highly regulated industries. For example, companies in healthcare, finance, or government sectors often prefer on-premise setups to guarantee that all dimensions of their security and data handling meet stringent compliance standards.
Investment and Operational Considerations
Despite its advantages, on-premise infrastructure demands a substantial upfront capital investment. Companies must purchase physical hardware, maintain secure facilities, and invest in cooling, power, and redundancy measures. This model also requires a larger internal IT workforce dedicated to ongoing maintenance, regular security updates, hardware lifecycle management, and routine security assessments.
Additionally, on-premise systems are often less flexible when it comes to scaling. To increase capacity, an organization must invest in additional hardware, which can be both time-consuming and costly. Combined with the need for physical space, this model can create challenges in environments where business demands are rapidly evolving.
Physical and Environmental Security
A significant advantage of on-premise security is the control over physical security elements. Organizations can safeguard their infrastructure using physical barriers, surveillance cameras, biometric access systems, and other measures designed to mitigate the risk of unauthorized access. However, this model is also vulnerable to physical disasters such as fires, floods, or power outages, making disaster recovery planning essential.
Cloud Security: Flexibility, Automation, and Cost Efficiency
Cloud security, by contrast, shifts the responsibility of infrastructure management to third-party providers who deliver computing resources over the internet. As companies migrate sensitive data and critical business applications to the cloud, the nature of security moves from physical hardware to virtualized resources and data centers maintained by experts.
Scalability and Rapid Deployment
One of the primary advantages of cloud security is its scalability. Cloud environments allow organizations to easily scale resources up or down according to fluctuating needs without the pain of investing in additional physical hardware. This on-demand model suits businesses that experience rapid growth or varying workloads, ensuring that resources—and the associated security measures—can adapt quickly.
Providers offer automated scaling along with maintenance and updates, which help reduce the daily operational burden on internal IT teams. This more flexible approach not only helps in cost management through a pay-as-you-go pricing model but also contributes to a more dynamic security posture.
Advanced Security Features and Monitoring
Cloud providers invest heavily in the latest security technologies and staff expertise. The robust security features typically include data encryption, advanced firewalls, comprehensive identity and access management, intrusion detection, and automated monitoring systems. Frequent updates and patches are seamlessly applied by the cloud provider, ensuring that the security environment remains current against emerging threats.
Despite these benefits, the delegation of security responsibilities introduces a shared responsibility model. While the provider maintains the security of the cloud, the organization is responsible for securing its applications and data within the cloud environment. This might require additional security measures and careful planning to prevent vulnerabilities that could stem from misconfiguration or insufficient internal policies.
Risk Management and Third-Party Dependencies
A significant factor to consider with cloud security is the dependency on the cloud vendor. While most leading providers maintain high standards of security and boast extensive certifications (like ISO 27001, GDPR, HIPAA), this external management can limit direct control over certain aspects of security management. Data breaches or misconfigurations at the provider level could expose sensitive information, making it critical for organizations to perform due diligence when selecting a cloud partner.
Moreover, cloud environments can sometimes be targeted for larger data breaches due to the aggregation of vast amounts of data on centralized servers. However, enhanced detection, quick mitigation capabilities, and elaborate incident response strategies deployed by cloud providers typically help reduce the risk and impact of such incidents.
Compliance and Regulatory Requirements
Both on-premise and cloud security environments can be engineered to comply with rigorous regulatory standards. However, the approach to compliance differs significantly between the two models.
On-Premise and Compliance
With on-premise security, organizations retain complete oversight of data locations and security measures. This is especially beneficial for industries where strict regulatory compliance is mandatory. For example, when handling sensitive personal data or critical financial information, the complete control over the physical and digital environment facilitates compliance with legal requirements. The ability to physically secure servers and manage access controls directly offers reassurance to regulators and stakeholders.
Cloud Compliance Considerations
Cloud providers are increasingly obtaining certifications and adhering to international standards such as GDPR, PCI DSS, and HIPAA. However, businesses must verify that the provider’s compliance measures align with their specific regulatory obligations. The inherent distributed nature of the cloud introduces complexities, especially when data resides in multiple jurisdictions. Organizations often adopt hybrid models to mitigate these risks—maintaining sensitive data on-premise while leveraging the cloud for less critical operations.
Cost Analysis and Operational Efficiency
When evaluating security approaches, it is crucial to consider the total cost of ownership (TCO) and operational efficiency. Both on-premise and cloud solutions have distinct cost structures and associated benefits.
On-Premise: Upfront Costs with Long-Term Management
The on-premise model usually requires significant capital expenditure at the outset. Costs include purchasing, setting up, and maintaining hardware, securing physical sites, and hiring specialized IT personnel. Over time, these systems incur additional expenses related to operational overhead, energy consumption, cooling, and routine upgrades. While these investments can be justified by the security customization and control they offer, they may also restrict the flexibility to quickly adjust to new or unexpected business demands.
Cloud: Pay-as-You-Go and Operational Efficiency
Cloud security tends to operate on a pay-as-you-go basis, which reduces the upfront financial burden. Organizations can allocate funds more dynamically, investing based on actual resource usage rather than committing large sums initially. This cost model enhances agility, making it easier for businesses to adapt to shifts in market demand or operational needs. However, subscription fees and cumulative costs over time need to be carefully managed and monitored to ensure that they remain within budgetary expectations.
Security Operation, Maintenance, and Monitoring
An essential aspect of maintaining digital security, whether on-premise or in the cloud, is the continuous operation and monitoring of security measures. Both environments require proactive strategies for identifying potential threats, handling incidents, and continuously verifying that all controls remain effective.
On-Premise Monitoring and Maintenance
Organizations managing on-premise infrastructures must invest significantly in skilled security teams who can conduct ongoing assessments and penetration tests. Regular audits, physical inspections, and the use of advanced monitoring tools are necessary to ensure any vulnerabilities are quickly identified and addressed. The reliance on a manual review process can, however, slow down response times during an incident.
Cloud-based Automated Security
Cloud environments benefit immensely from automation. Tools integrated into cloud platforms can automatically patch vulnerabilities, update security protocols, and detect anomalies in real time. This automated approach reduces some of the heavy lifting required by in-house teams and helps ensure that security updates are applied consistently. Nonetheless, organizations must not entirely forgo their responsibility; ensuring that cloud assets are properly configured and secured remains paramount.
Comparative Security Table
The table below provides a side-by-side comparison of key attributes of on-premise and cloud security environments:
| Attribute | On-Premise Security | Cloud Security |
|---|---|---|
| Control | Full direct control; in-house customization and management | Limited control; relies on provider’s standardized security framework |
| Scalability | Requires investment in hardware; less flexible | Highly scalable with on-demand resource allocation |
| Cost Structure | High upfront costs; ongoing maintenance expenses | Lower initial investment; subscription-based with potential cumulative cost |
| Compliance Flexibility | Greater capacity to tailor to strict regulatory controls | May require additional measures to meet specific compliance needs |
| Maintenance & Updates | Manually driven by internal teams | Automated, frequent updates managed by providers |
| Risk & Disaster Preparedness | Vulnerable to physical disasters; requires local redundancies | Enhanced redundancy and backup systems; shared risk model |
Choosing the Appropriate Model
Deciding between on-premise and cloud security environments involves a thorough evaluation of organizational needs, risk tolerance, and long-term business goals. For companies that require highly customized, controlled security and have the resources to maintain a dedicated IT team, on-premise security might be the better choice. This model is especially relevant for organizations in sectors that demand strict compliance and monitoring, such as financial institutions, healthcare providers, and government agencies.
Conversely, businesses looking to enhance agility, reduce capital expenditure on physical resources, and leverage advanced, automated security features might prefer cloud security. Many organizations today implement hybrid approaches that blend both models, hosting sensitive systems on-premise while taking advantage of the scalability and flexibility of the cloud for less critical applications. This hybrid strategy provides a risk-mitigated balance, ensuring that the most sensitive operations are maintained internally while still benefiting from the cloud’s efficiencies.
References
- Cloud vs On-Premise Security - DNSstuff
- On-Premise vs. Cloud Security - TechRepublic
- Cloud vs. On-Premise Security - SentinelOne
- Cloud vs. On-Premise Security - Avigilon
-
Cloud vs. On-Premise Security - Accuknox
Recommended Searches
Last updated March 14, 2025