
How to Spoof the X-Forwarded-For Header
A Comprehensive Guide to HTTP Header Manipulation
Key Takeaways
- Understanding HTTP Headers: The `X-Forwarded-For` header is used to identify the originating IP address of a client connecting to a server through a proxy or load balancer.
- Methods of Spoofing: Various tools and techniques can be used to modify the `X-Forwarded-For` header, including command-line tools and browser extensions.
- Security and Ethical Considerations: Spoofing headers can have significant security implications and may be illegal; it should only be done for educational or authorized testing purposes.
Introduction to X-Forwarded-For Header
The `X-Forwarded-For` (XFF) header is a common HTTP header field used to identify the original IP address of a client connecting to a web server through an HTTP proxy or a load balancer. This header is particularly useful in scenarios where a client's request passes through multiple intermediaries before reaching the server. The XFF header is crucial for logging, analytics, and access control purposes, as it allows servers to track the original source of the request despite the involvement of proxies.
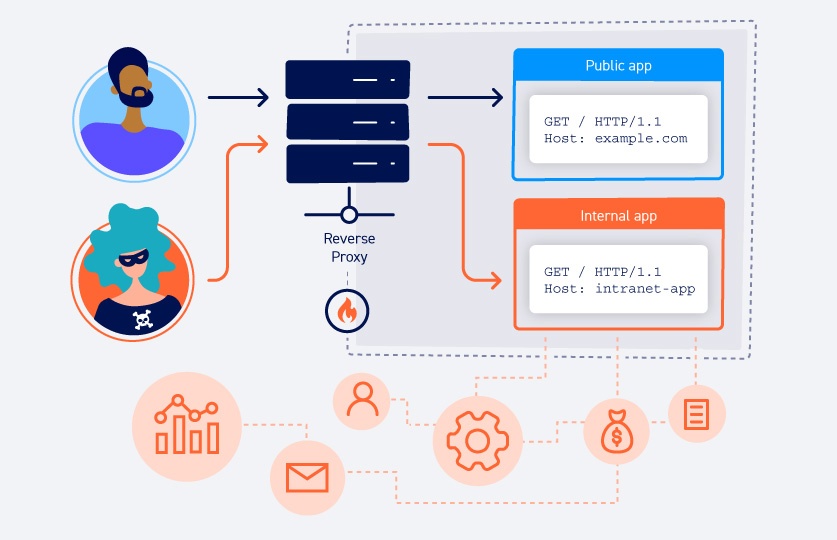
However, the XFF header's reliance on client or intermediary input makes it vulnerable to spoofing. By altering this header, an attacker can potentially mask their real IP address, bypass IP-based access controls, or inject false data into server logs. Understanding how to manipulate this header is essential for security professionals to develop effective countermeasures and for developers to ensure their applications are not susceptible to such attacks.
Methods of Spoofing the X-Forwarded-For Header
Using Browser Plugins
Browser extensions like ModHeader can be used to modify HTTP headers directly from within the browser. This method is straightforward and suitable for educational purposes or testing configurations. Here are the steps to spoof the XFF header using a browser plugin:
- Install a browser plugin capable of modifying HTTP headers, such as ModHeader.
- Configure the plugin to add or replace the `X-Forwarded-For` header with a desired IP address.
- Navigate to the target website or application to send requests with the modified header.
Using cURL Commands
The cURL command-line tool is widely used for making HTTP requests and can easily be used to spoof the XFF header. Here's how to use cURL to modify the header:
curl -H "X-Forwarded-For: 123.45.67.89" http://example.comThis command sends a request to `example.com` with the `X-Forwarded-For` header set to the specified IP address.
Programmatic Manipulation Using Proxies or Middleware
Programmatically altering the XFF header can be achieved through the use of proxies or middleware. This method is useful for developers who need to simulate various scenarios or test security configurations. Below is an example of how to spoof the XFF header using Python with the `requests` library:
import requests

headers = {
    'X-Forwarded-For': '123.45.67.89'
}
response = requests.get('http://example.com', headers=headers)
print(response.text)
Using Local HTTP Proxy Tools
Tools such as Burp Suite or OWASP ZAP can intercept and modify HTTP requests, including the XFF header, before they reach the server. Here's how to use such a tool:
- Configure your browser or application to route traffic through the proxy tool.
- Intercept the request using the tool.
- Modify the `X-Forwarded-For` header to a spoofed IP address.
- Forward the modified request to the server.
Direct Header Modification in Backend APIs
When developing server-side applications, developers can directly modify the XFF header before making requests to another API. Here's an example in Node.js using the `axios` library:
const axios = require('axios');

axios.get('http://example.com', {
    headers: { 'X-Forwarded-For': '123.45.67.89' }
}).then(response => {
    console.log(response.data);
});
Security Implications of Spoofing the X-Forwarded-For Header
Risks and Vulnerabilities
Spoofing the XFF header poses several risks to both clients and servers:
- Unauthorized Access: By altering the XFF header, attackers can bypass IP-based access controls, potentially gaining unauthorized access to restricted resources.
- Inaccurate Logging: Spoofed headers can lead to incorrect logging, making it difficult to trace the actual source of requests and potentially hiding malicious activities.
- Blind XSS Attacks: Injecting malicious data into the XFF header can be used to launch Blind Cross-Site Scripting (XSS) attacks, exploiting vulnerabilities in server-side code that processes this header.
Legal and Ethical Considerations
Spoofing the XFF header can have serious legal and ethical implications:
- Legal Risks: Deliberately spoofing headers to gain unauthorized access or engage in malicious activities can be illegal under laws like the Computer Fraud and Abuse Act (CFAA).
- Ethical Concerns: Such actions may violate terms of service, corporate security policies, and data protection regulations, potentially leading to sanctions or legal action.
- Authorized Testing: Spoofing for educational purposes or authorized security testing is acceptable but should be conducted with caution and proper authorization.
Prevention Strategies
Validating and Sanitizing Headers
To prevent XFF header spoofing, servers should validate and sanitize incoming headers:
- IP Address Validation: Ensure that the XFF header contains a valid IP address format.
- Header Sanitization: Remove or sanitize any unexpected or malicious data in the header to prevent injection attacks.
Disabling Unnecessary HTTP Methods
Disabling HTTP methods like `TRACE` can help reduce the risk of information leakage that could be exploited by attackers.
Implementing Secure Protocols
Enforcing the use of HTTPS can protect against man-in-the-middle attacks, which are often used to intercept and modify HTTP headers.
Rate Limiting and Access Controls
Implementing IP-based rate limiting and access controls can mitigate the impact of spoofed headers by limiting the number of requests from a single IP address.
Advanced Techniques for Spoofing and Detection
Exploiting Proxy Chains
Attackers can use multiple proxies to create a chain of XFF headers, making it challenging to identify the real IP address. This technique involves appending fake IP addresses to the XFF header as it passes through different proxies.
Injecting Malicious Data
Injecting non-IP data or garbage values into the XFF header can cause errors or log injection attacks. This technique can be used to disrupt server operations or hide malicious activities.
Detecting Spoofed Headers
Detecting spoofed XFF headers requires a combination of techniques:
- Header Consistency Checks: Compare the XFF header with other headers like `X-Real-IP` or `Client-IP` to detect inconsistencies.
- IP Reputation Services: Use IP reputation services to identify known malicious IP addresses.
- Behavioral Analysis: Monitor request patterns and behaviors to detect anomalies that may indicate spoofing.
Case Studies and Real-World Examples
OAuth Callback IP Spoofing
A notable example of XFF header manipulation was observed in an OAuth callback scenario. An attacker used a manipulated XFF header to spoof an IP address, tricking the server into believing the request came from a different IP. This vulnerability was exploited to bypass security checks and gain unauthorized access to protected resources.
Web Application Firewall Bypass
Some attackers have used XFF header spoofing to bypass Web Application Firewalls (WAFs). By injecting fake IP addresses, they could evade IP-based rate limiting and access controls, allowing them to launch more aggressive attacks against the target application.
Best Practices for Developers
Secure Implementation of X-Forwarded-For Headers
Developers should follow best practices when implementing XFF headers in their applications:
- Use Trusted Proxies: Only accept XFF headers from trusted proxies, such as AWS ELB or dedicated reverse proxies.
- Implement Header Validation: Validate and sanitize incoming XFF headers to prevent spoofing and injection attacks.
- Log and Monitor: Log all XFF headers and monitor for anomalies to detect potential spoofing attempts.
Educational and Testing Scenarios
For educational or testing purposes, developers can safely experiment with XFF header manipulation in controlled environments:
-
Use Virtual Environments: Set up virtual environments or test labs to simulate different scenarios without affecting production systems.
-
Obtain Proper Authorization: Ensure that any testing or experimentation is authorized by the relevant stakeholders and complies with legal and ethical standards.
Conclusion
Spoofing the `X-Forwarded-For` header is a technique that can be used to manipulate the perceived source of an HTTP request. While this can be useful for educational purposes or authorized security testing, it poses significant security risks and can be illegal if used maliciously. Understanding how to spoof this header is crucial for developers and security professionals to implement effective defenses and ensure the integrity of their systems.
References
| Method | Description | Tools | Security Implications |
|---|---|---|---|
| Browser Plugins | Modify headers directly from within the browser | ModHeader | Risk of unauthorized access, inaccurate logging |
| cURL Commands | Use command-line tool to set headers | cURL | Potential for bypassing IP-based controls |
| Programmatic Manipulation | Modify headers in code using proxies or middleware | Python (requests), Node.js (axios) | Risk of injection attacks, unauthorized access |
| Local HTTP Proxy Tools | Intercept and modify headers before sending to server | Burp Suite, OWASP ZAP | Can lead to inaccurate logging, Blind XSS attacks |
| Backend API Modification | Modify headers directly in server-side code | Node.js (axios) | Risk of unauthorized access, inaccurate logging |
Last updated February 2, 2025