
Unlock Ultimate Cookie Security: How to Consistently Enforce SameSite=Strict in Nginx
Tired of inconsistent cookie settings? Learn the definitive methods to configure Nginx for robust SameSite=Strict enforcement.
Ensuring that cookies are handled securely is paramount for web application safety. The SameSite=Strict attribute is a powerful tool in preventing Cross-Site Request Forgery (CSRF) attacks by restricting cookies to first-party contexts only. However, achieving consistent enforcement across all cookies, including session cookies and those set for specific paths, can be challenging when using Nginx as a reverse proxy.
This guide provides a comprehensive overview of how to configure Nginx to reliably add or modify the Set-Cookie header, ensuring the SameSite=Strict attribute is applied uniformly.
Key Insights for Nginx Cookie Management
- Importance of
SameSite=Strict: This attribute provides the highest level of protection against CSRF by ensuring cookies are only sent with requests originating from the same site. - Modern Nginx Solution (
proxy_cookie_flags): For Nginx versions 1.19.3 and later, theproxy_cookie_flagsdirective offers a native and flexible way to manage cookie attributes likeSameSite,Secure, andHttpOnly. - Solutions for Older Nginx Versions: If you're using an older Nginx version, alternative methods include the
proxy_cookie_pathdirective (as a limited workaround) or installing a third-party module likenginx_cookie_flag_modulefor more precise control.
Understanding the SameSite Cookie Attribute
The SameSite attribute dictates whether a browser should send cookies with cross-site requests. It aims to mitigate security risks associated with cookies being sent unintentionally.
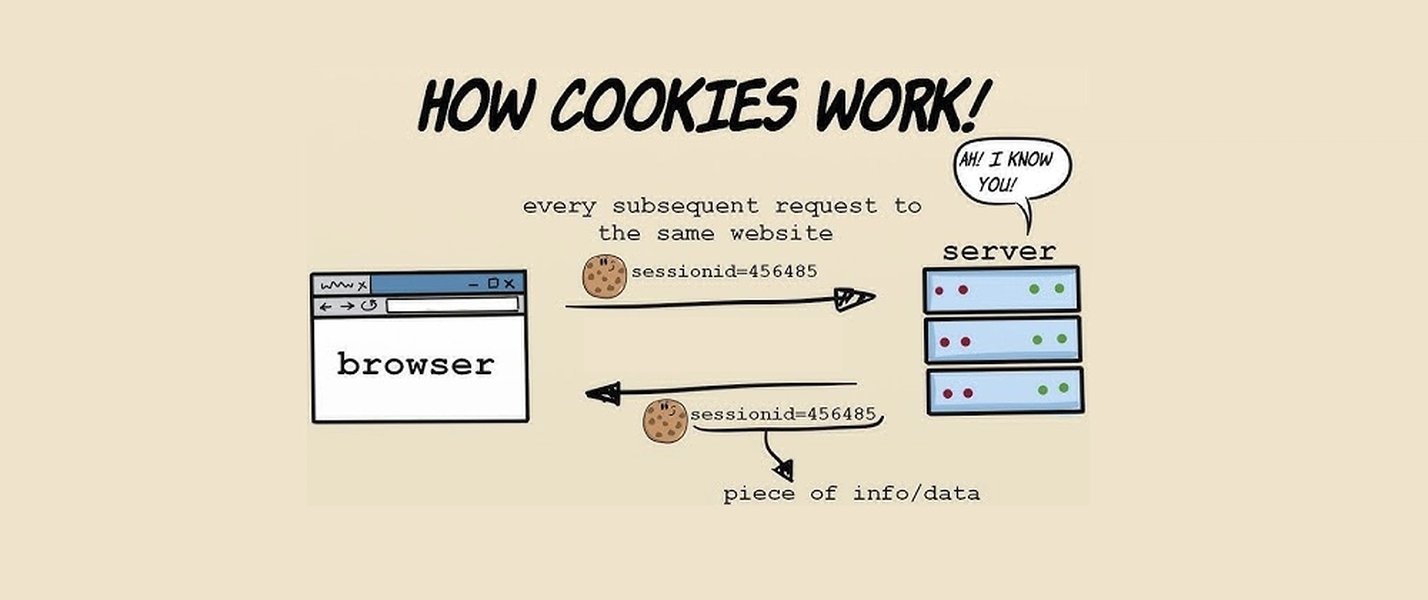
Visual representation of HTTP Cookies.
Attribute Values Explained:
- Strict: Cookies are only sent in a first-party context. They are withheld on cross-site navigation, even when following a link. This offers the strongest security against CSRF but can sometimes affect user experience if links from external sites rely on session cookies.
- Lax: Cookies are withheld on cross-site subrequests (e.g., calls to load images or frames) but are sent when a user navigates to the origin site from an external site (e.g., by following a link). This is the default behavior in many modern browsers if no
SameSiteattribute is specified. - None: Cookies are sent on both same-site and cross-site requests. To use
SameSite=None, theSecureattribute must also be set, meaning the cookie can only be sent over HTTPS. This is necessary for cookies intended for cross-site usage but requires careful consideration due to potential security implications.
Enforcing SameSite=Strict is generally recommended for sensitive cookies like session identifiers to provide maximum protection.
Configuring Nginx for SameSite=Strict Enforcement
Nginx, acting as a reverse proxy, can intercept responses from upstream applications and modify the Set-Cookie headers before they reach the client's browser. The best method depends on your Nginx version.
Method 1: Using proxy_cookie_flags (Nginx 1.19.3+)
This is the recommended approach for modern Nginx installations. The proxy_cookie_flags directive allows direct manipulation of cookie flags.
Applying to All Cookies:
To apply SameSite=Strict, Secure, and HttpOnly flags to all cookies passed from the upstream server, use the following configuration within your location or server block:
location / {
    proxy_pass http://your_backend_app;
    # Apply flags to all cookies (using '~' regex)
    proxy_cookie_flags ~ samesite=strict secure httponly;
}
Applying to Specific Cookies:
If you only need to target specific cookies (e.g., a session cookie named SESSIONID), you can specify the cookie name or use a more targeted regular expression:
location / {
    proxy_pass http://your_backend_app;
    # Apply flags only to cookies named 'SESSIONID'
    proxy_cookie_flags SESSIONID samesite=strict secure httponly;

    # Apply flags to cookies whose names contain 'session' (case-insensitive)
    # proxy_cookie_flags ~*session samesite=strict secure httponly;
}
This directive offers fine-grained control and is the cleanest way to manage cookie attributes in newer Nginx versions.
Method 2: Using proxy_cookie_path (Older Nginx Versions - Workaround)
For Nginx versions prior to 1.19.3, the proxy_cookie_flags directive is unavailable. A common, though less ideal, workaround involves using the proxy_cookie_path directive. This directive primarily changes the Path attribute of a cookie but can be leveraged to append other attributes.
location / {
    proxy_pass http://your_backend_app;
    # Appends attributes to the Path; may have unintended side effects
    proxy_cookie_path / "/; SameSite=Strict; Secure; HttpOnly";
}
Caution: This method essentially overwrites the cookie's path and appends the flags. It might work for simple cases but can be unreliable or cause issues if cookies rely on specific paths. It applies broadly and lacks the precision of proxy_cookie_flags.
Method 3: Using the nginx_cookie_flag_module (Third-Party Module)
For older Nginx versions requiring more robust control than proxy_cookie_path allows, the third-party nginx_cookie_flag_module (also known as the Cookie-Flag dynamic module) is a viable option. This module needs to be compiled with Nginx or loaded dynamically.
Installation and Configuration:
- Install the module (refer to its documentation, e.g., from GitHub or Nginx Extras).
- Load the module in your main
nginx.conffile:load_module modules/ngx_http_cookie_flag_filter_module.so; - Use the
set_cookie_flagdirective in yourlocationorserverblock:location / { proxy_pass http://your_backend_app; # Apply SameSite=Strict and Secure to a specific cookie set_cookie_flag SessionID SameSite=Strict Secure; # Apply SameSite=Strict to all cookies (using '*') set_cookie_flag * SameSite=Strict HttpOnly; }
This module provides functionality similar to proxy_cookie_flags and is a good solution if upgrading Nginx is not feasible.
Visualizing Nginx SameSite Configuration Approaches
The following mindmap illustrates the different strategies for enforcing SameSite=Strict in Nginx, depending on your version and requirements.
proxy_cookie_flags (Native)"]
id1a1["Apply to all cookies: ~"]
id1a2["Apply to specific cookies: CookieName or ~regex"]
id1a3["Combine with Secure and HttpOnly"]
id1a4["Recommended Method"]
id2["Nginx Version < 1.19.3"]
id2a["Use proxy_cookie_path (Workaround)"]
id2a1["Appends attributes to Path"]
id2a2["Less precise, potential side effects"]
id2a3["Example: proxy_cookie_path / \"/; SameSite=Strict; Secure\""]
id2b["Use nginx_cookie_flag_module (Third-Party)"]
id2b1["Requires module installation/loading"]
id2b2["Use set_cookie_flag directive"]
id2b3["Supports wildcards (*) and specific names"]
id2b4["Provides granular control"]
id3["General Considerations"]
id3a["Importance of Secure Flag (HTTPS)"]
id3b["Upstream Application Settings"]
id3c["Testing and Verification (DevTools)"]
id3d["Handling Session Cookies & Specific Paths"]
Comparing Nginx SameSite Configuration Methods
Choosing the right method depends on factors like your Nginx version, the level of control needed, and ease of implementation. The radar chart below compares the three main approaches based on key characteristics.
As the chart illustrates, proxy_cookie_flags generally offers the best balance for modern Nginx setups, while the third-party module is a strong contender if you're on an older version and need precise control. The proxy_cookie_path method serves as a simpler, albeit less reliable, fallback.
Addressing Inconsistencies and Best Practices
You mentioned that SameSite=Strict wasn't being applied consistently, especially for session cookies or specific paths. Here's how to tackle that:
Potential Causes for Inconsistency
- Upstream Application Behavior: The backend application might be setting cookies without the necessary attributes, or overwriting headers in a way that bypasses Nginx rules. Ensure your application-level cookie settings are appropriate or rely solely on Nginx for enforcement.
- Nginx Configuration Scope: Ensure the directive (
proxy_cookie_flags,proxy_cookie_path, orset_cookie_flag) is placed within the correctlocationblock that handles the requests setting the cookies (e.g.,/,/login,/api). Rules in one location block won't affect others unless inherited. - Conflicting Rules: Check for other Nginx directives that might interfere, such as
add_header Set-Cookie ...(which can overwrite) orproxy_hide_header Set-Cookie. - Targeting Specific Cookies: If a global rule (
~or*) isn't catching specific session cookies, try targeting them explicitly by name usingproxy_cookie_flags CookieName ...orset_cookie_flag CookieName ....
Best Practices
- Always Use HTTPS: While
SameSite=Strictdoesn't strictly require theSecureflag (unlikeSameSite=None), enforcing HTTPS across your site is crucial for overall security. CombiningSameSite=StrictwithSecureis highly recommended. - Include
HttpOnly: For cookies not needed by client-side JavaScript (like session cookies), always add theHttpOnlyflag to prevent access via script, mitigating XSS risks. - Test Thoroughly: After applying changes, test your application extensively. Check login flows, session persistence, and any functionality relying on cookies, especially across different browsers.
- Verify with Developer Tools: Use your browser's developer tools (Network tab or Application > Cookies tab) to inspect the
Set-Cookieheaders in the response and verify that cookies have the desiredSameSite=Strict,Secure, andHttpOnlyattributes.

Use browser developer tools to inspect cookie attributes.
Nginx Directive Summary for Cookie Attribute Management
This table summarizes the primary Nginx directives and modules discussed for managing cookie attributes like SameSite.
| Directive / Module | Syntax Example | Nginx Version | Use Case | Notes |
|---|---|---|---|---|
proxy_cookie_flags |
proxy_cookie_flags ~ samesite=strict secure; |
1.19.3+ | Modify flags (SameSite, Secure, HttpOnly) for proxied cookies. | Recommended native method for modern Nginx. Supports regex and specific names. |
proxy_cookie_path |
proxy_cookie_path / "/; SameSite=Strict"; |
All versions | Rewrite cookie Path; can append attributes as a workaround. | Limited, less reliable for flag setting. Can have side effects on the Path attribute. |
set_cookie_flag (from module) |
set_cookie_flag SessionID SameSite=Strict Secure; |
Requires module install | Fine-grained control over cookie flags, similar to proxy_cookie_flags. |
Excellent alternative for older Nginx versions needing precise control. Requires setup. |
add_header |
add_header Set-Cookie "mycookie=value; SameSite=Strict"; |
All versions | Add a *new* Set-Cookie header. | Generally not suitable for modifying existing upstream cookies; can cause duplicates or overwrite issues. |
Understanding Cookie Security Concepts
This video provides a good overview of cookie security parameters, including the importance of attributes like SameSite, Secure, and HttpOnly.
The video delves into how these attributes help protect against common web vulnerabilities, reinforcing why careful configuration, such as enforcing SameSite=Strict, is essential.
Frequently Asked Questions (FAQ)
What exactly does SameSite=Strict prevent?
SameSite=Strict prevents the browser from sending the cookie along with any cross-site requests. This means the cookie is only sent when the request originates from the same domain that set the cookie. It effectively blocks CSRF attacks that rely on tricking a user's browser into sending authenticated requests to your site from a malicious site.
Why should I use Nginx to set `SameSite` instead of my application?
While it's ideal for the application itself to set correct cookie attributes, using Nginx offers several advantages:
- Consistency: Nginx can enforce rules uniformly across all upstream applications it proxies, even if those applications have inconsistent or outdated cookie settings.
- Centralized Management: Security policies can be managed at the edge (reverse proxy) level, simplifying configuration and updates.
- Legacy Applications: For older applications that are difficult to modify, Nginx provides a way to enhance cookie security without code changes.
However, the best approach often involves setting attributes correctly at the application level and using Nginx as a secondary enforcement layer.
My Nginx version is older than 1.19.3. What's the best option?
If you cannot upgrade Nginx, the most reliable option is to install and use the third-party `nginx_cookie_flag_module`. It provides `set_cookie_flag`, which offers granular control similar to the native `proxy_cookie_flags`. Using `proxy_cookie_path` is a simpler alternative but less precise and potentially problematic. Consider upgrading Nginx if possible to leverage native features.
Is the `Secure` flag required when using `SameSite=Strict`?
Unlike `SameSite=None`, the `SameSite=Strict` attribute itself does not technically require the `Secure` flag to function according to the standard. However, sending sensitive cookies (like session IDs) over unencrypted HTTP is a major security risk regardless of the `SameSite` setting. Therefore, it is strongly recommended to always use HTTPS for your entire site and include the `Secure` flag on all sensitive cookies, including those marked `SameSite=Strict`.
How can I definitively check if `SameSite=Strict` is working correctly?
Use your browser's developer tools:
- Open the Developer Tools (usually F12).
- Go to the "Network" tab and reload the page that sets the cookie. Find the request responsible for setting the cookie (e.g., the main page load or a login request). Check the `Set-Cookie` header in the "Response Headers" section.
- Alternatively, go to the "Application" (or "Storage") tab, find "Cookies" under the site's domain, and inspect the "SameSite" column for the relevant cookies. It should show "Strict".
- Test cross-site scenarios (e.g., linking from another domain) to confirm the cookie is not sent when it shouldn't be.
Recommended Further Exploration
- How does Nginx proxy_cookie_flags work with regular expressions for targeting cookies?
- Compare SameSite Strict vs Lax security implications in detail.
- What are the steps to install and configure the nginx_cookie_flag_module on Ubuntu?
- What are the best practices for overall session cookie security in web applications?
References
Last updated May 2, 2025